A governed MCP data-access pattern separates tool interaction from permission to receive enterprise data. Connect the host and MCP server to an explicitly authorized data-product interface, then keep identity, record and field constraints, freshness and evidence visible across that path.
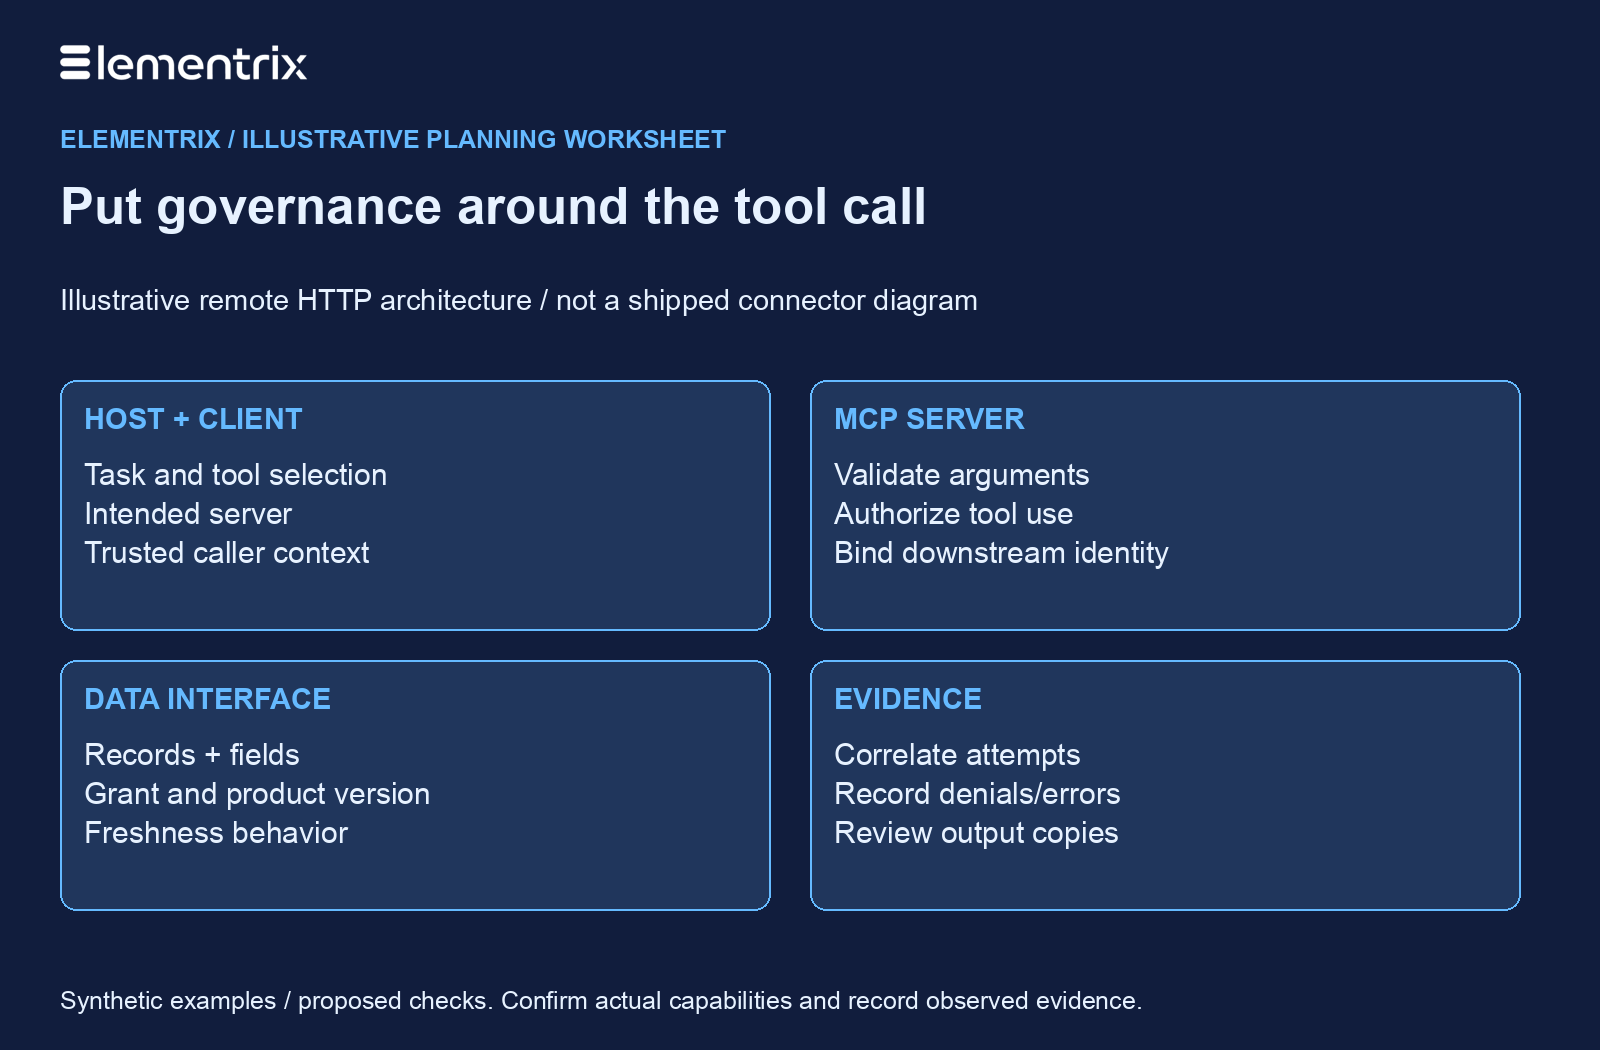
Map the participants and the trust boundaries
The official MCP architecture overview for version 2026-07-28 describes a host coordinating clients that connect to servers. Servers expose context capabilities such as tools. The protocol organizes the interaction; it does not supply an enterprise’s business entitlement model.
For the pattern below, consider a remote HTTP MCP server exposing a narrowly scoped customer-status tool. The host runs the AI application, a client manages protocol interaction, the server validates and executes the tool request, and a governed data interface resolves permitted data. This is an illustrative architecture proposal, not a claim that an Elementrix MCP connector or every depicted control is shipped.
| Component | Responsibility | Review question |
|---|---|---|
| Host and client | Select the intended server and coordinate interaction | Which tools and identities can this task use? |
| MCP server | Validate tool input and bind a trusted caller context | Can model-supplied arguments expand the grant? |
| Data-product interface | Authorize records, fields and operations before delivery | What exact representation is allowed? |
| Source and refresh path | Produce a defined product version and timestamp | Can freshness be evaluated reliably? |
| Evidence path | Correlate the tool attempt with downstream decisions | Can an operator reconstruct a specific request? |
Keep discovery separate from consumption
A visible tool name is not evidence that the caller may retrieve every record available to it. Tool metadata can help the host understand an operation, but execution must still validate the identity, intended resource and permitted arguments. Conversely, hiding a tool in the interface is insufficient if an unauthorized caller can invoke its server route directly.
Keep the exposed tool narrow enough to review. A customer-status read with bounded selectors is easier to reason about than an unrestricted query string. Validate record identifiers and field requests at a trusted boundary. Do not treat model output as an authoritative approval or grant revision.
Specify the data boundary before wiring the tool
| Contract element | Proposed value | Required validation |
|---|---|---|
| Consumer | routing-assistant application | Trusted application identity; delegated employee if relevant |
| Purpose | Route assigned support tasks | Purpose agreed by owner; caller text cannot create approval |
| Records | Assigned north-region accounts | Check record boundary on each applicable read |
| Fields | customer_id, account_status, service_region | Exclude contact and financial properties |
| Freshness | Owner-defined age budget | Compare a meaningful product timestamp with the requirement |
| Evidence | Tool-attempt and runtime-request references | Link to the resolved grant and product version |
Choose how to handle unavailable or stale data before launch. An expired product timestamp may require a clearly marked degraded response or a refusal for a sensitive workflow. The model should not silently substitute an old answer. Confirm that the data interface exposes enough metadata to enforce the chosen rule. An arbitrary server-receipt timestamp is not the same as source freshness.
Walk through one illustrative interaction
{
  "example_type": "synthetic protocol-neutral interaction",
  "tool_intent": "read_customer_status",
  "customer_ref": "SYN-022",
  "approved_result": {
    "customer_id": "SYN-022",
    "account_status": "active",
    "service_region": "north"
  },
  "evidence_ref": "EXAMPLE-TOOL-022"
}
This JSON describes the design intent, not a wire-level MCP request, a real endpoint or an executed test. The server must resolve the caller’s actual permission rather than accepting approved_result from the model. A response can include an evidence reference only when the implementation can produce and protect the corresponding record.
Trace the interaction in order: the client reaches the intended server; the server validates the tool inputs; the data interface evaluates the relevant grant and product version; the permitted representation is constructed; and the host receives only that representation. Record a denial or dependency error distinctly from a completed read.
Review the failure cases across the whole path
- Wrong server or token audience: reject at the corresponding authentication boundary.
- A tool argument requests an excluded property: enforce the field contract before returning values.
- The model asks for a different tenant or customer: check the record boundary.
- The grant changes during a session: verify subsequent requests and caches.
- The source becomes stale or unavailable: follow the documented task-specific behavior.
- A value enters history, logs, exports or an index: review these downstream copies separately.
Use synthetic fixtures and record actual observations for each route. A plausible generated answer does not prove that the underlying access boundary worked. Review the server-side decision and delivered payload alongside the host’s behavior. The authorization and testing guides linked below develop these narrower questions.
Bring the proposed component map to the implementation team. Ask which parts the intended deployment provides, which require integration and which remain organizational responsibilities. That discussion makes a supported integration demonstration more useful than a generic connector diagram.
For related implementation detail, see governed AI data access overview; AI governance context; Application-Level vs User-Level Data Access; Data Access Audit Trail: What Evidence Should You Capture?.
For the permission layers, use the MCP and downstream authorization guide. To exercise the complete consumer, use the AI agent permission test checklist.
Discuss your scoped use case
Discuss a governed AI consumer; request a supported integration demo.