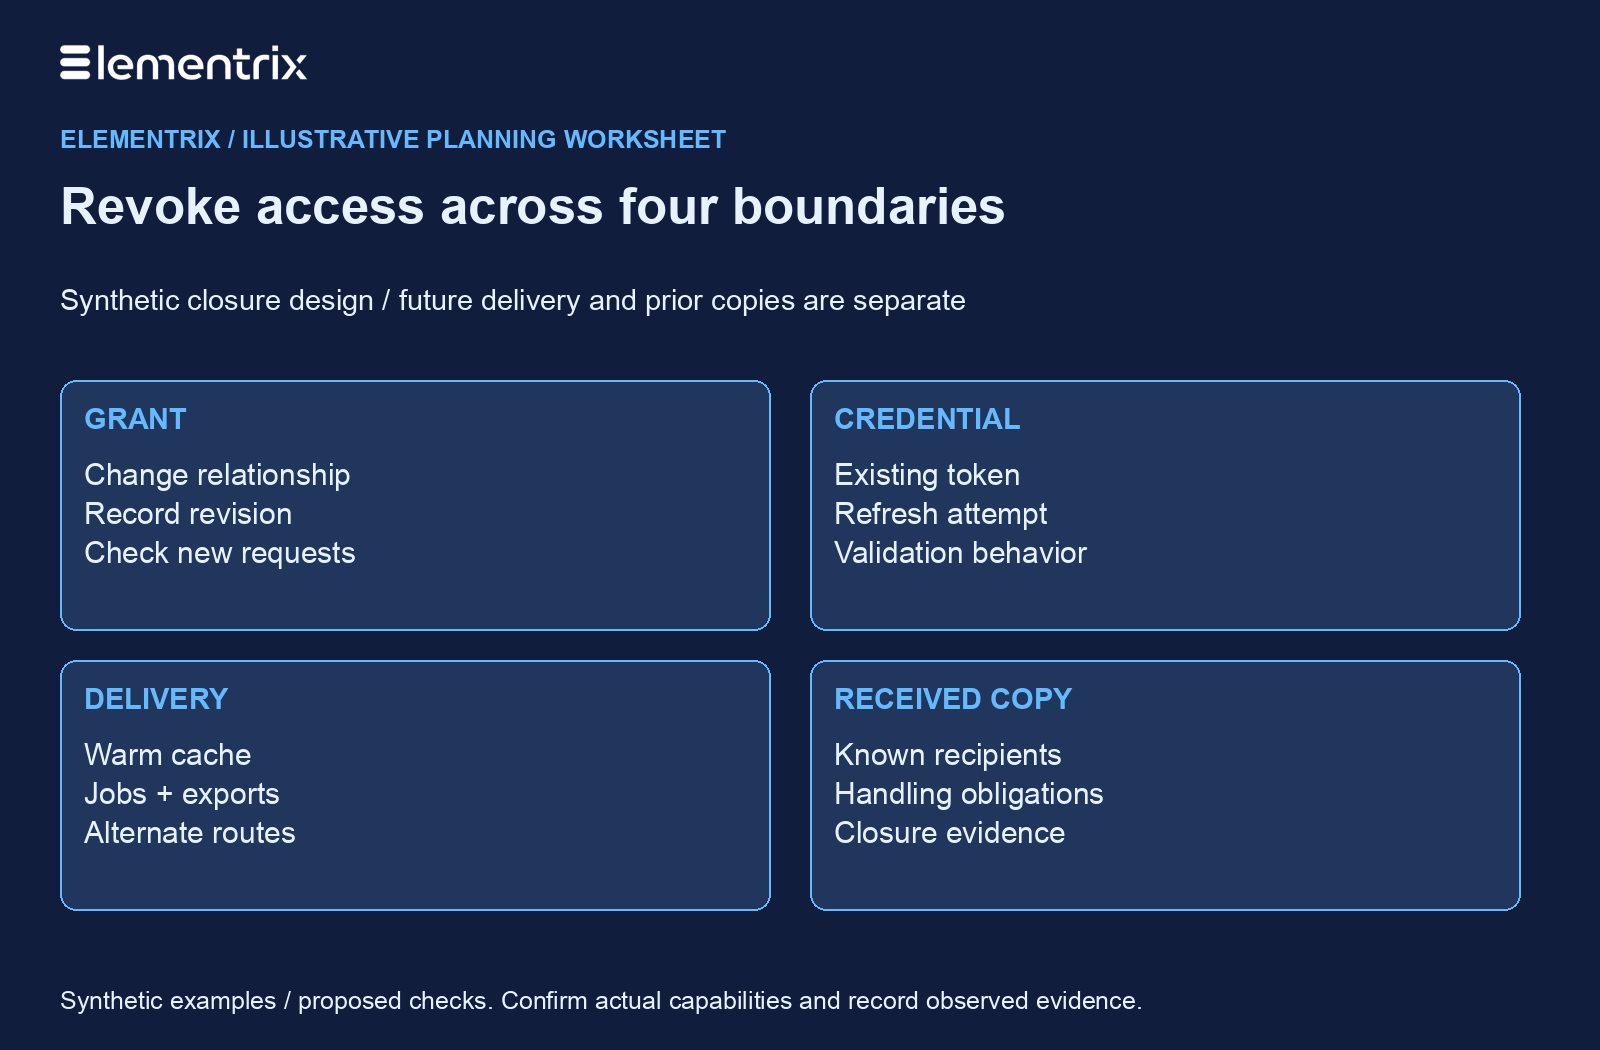
Data access revocation should stop future unauthorized delivery across every active path. Removing a grant, invalidating a token, preventing cached delivery and handling copies already received are distinct tasks. Define the boundary and verification evidence for each before promising a completion time.
Define what must stop and when
A partner contract ends at a specified time. Does that mean no new API request may start, an in-flight export must be cancelled, refresh tokens must stop minting access tokens, or previously delivered data must be handled under a closure process? Write each requirement separately. Otherwise a successful administration action can conceal a still-active delivery route.
Choose an accountable revocation owner and a clock reference. Record the request time, decision time, each enforcement change and the last verified access attempt. If different services propagate permission changes asynchronously, measure their behavior and state the remaining uncertainty. A desired target is not a measured guarantee.
| Boundary | Action to assess | Verification |
|---|---|---|
| Grant or entitlement | Disable the relevant consumer-product relationship | A new read under that relationship is denied |
| Access and refresh tokens | Apply the authorization server’s supported revocation behavior | Existing token and refresh attempt checked separately |
| Authorization cache | Invalidate or version stale permission decisions | A warm-path request resolves the changed permission |
| Response and data cache | Keep authorization ahead of delivery; remove unsafe entries as needed | Cached data is not served under an obsolete grant |
| Exports, jobs and subscriptions | Stop pending work and scheduled delivery where required | Queue, download link and alternate route checked |
| Received copies | Identify recipients, obligations and closure evidence | Recipient handling recorded; no unsupported recall claim |
Treat token revocation as one component
RFC 7009 defines an OAuth token-revocation mechanism. Its existence does not establish how every resource server or self-contained access token in a particular deployment detects a change. Confirm token lifetime, validation, introspection or other supported enforcement behavior with the implementation.
Test the old credential as well as a newly acquired one. Removing a refresh token may prevent future tokens while an already-issued access token remains usable under the service’s validation rules. Do not store credentials in the test report: use a protected reference to the credential fixture and record only the relevant outcome.
Make cache behavior part of the closure plan
A cache contains data; it should not independently decide that a former consumer may still receive it. Place a fresh, appropriate authorization check before returning protected cached content. If authorization decisions themselves are cached, document the complete decision key, revision strategy and permitted lifetime. Invalidation must cover the actual replicas and routes used in delivery.
Use a controlled synthetic record to warm the cache before revocation. Repeat the read afterward through each serving path. A cold-cache denial alone cannot demonstrate that a warm cached response is safe. The OWASP web-cache security guidance is useful when reviewing application and shared cache boundaries.
Walk through a synthetic revocation timeline
| Step | Owner | Evidence to keep |
|---|---|---|
| T0: authorized closure requested | Data owner | Consumer, product, reason, scope and requested effective time |
| T1: grant changed | Platform operator | Grant revision and implementation outcome |
| T2: credential and route actions applied | Identity and delivery owners | Token handling, cache actions, jobs and download-link state |
| T3: new attempts exercised | Independent verifier | Denied read, warm-cache check and refresh attempt with timestamps |
| T4: received-copy handling reviewed | Consumer owner | Known extracts, retention obligations and unresolved exceptions |
| T5: closure accepted or escalated | Accountable owner | Actual observations, gaps, next action and reviewer |
Suppose partner-router previously read customer_id, account_status and service_region for assigned north-region records. The closure test should retry that exact relationship, attempt an export and check any background subscription. A successful denial for an unrelated account is weak evidence. Leave the closure record open if an authorized requirement is still unverified.
Separate future access from prior possession
Stopping the API does not erase a response already delivered to a recipient, a spreadsheet downloaded earlier or a derived store built from an export. Inventory these copies during onboarding so closure is possible later. Assign a recipient contact and agreed handling process rather than treating a server-side permission change as evidence of deletion.
Record which copies are known, which are outside the platform’s technical reach and which closure evidence was actually obtained. Requirements depend on the agreement and the applicable organizational context; this checklist supplies an operating structure, not a universal retention duration or legal conclusion.
Use a completion checklist
- Enumerate consumers, delegated identities, products and operations affected.
- Record the authoritative permission change and credential treatment.
- Exercise new reads, cached paths, in-flight work and alternate exports.
- Compare actual observations with the agreed effective-time requirement.
- Document received-copy obligations, exceptions, owner and follow-up date.
Run this procedure in a controlled environment before depending on it in an incident. Where the test reveals a propagation gap, fix the specific enforcement path and repeat the same scenario. Do not replace missing evidence with an “instant revocation” label.
For related implementation detail, see field-level security; access management lifecycle; data access control; Partner Data Onboarding: A Governed Access Checklist; Data Access Audit Trail: What Evidence Should You Capture?; How to Test Field-Level API Permissions.