Data access management is the lifecycle for deciding, delivering, reviewing and ending access to data. It connects a business purpose and an identified consumer to an approved set of records, fields and operations. A complete process answers more than who can log in: it shows who approved access, what was actually delivered, when the need should be reviewed and how access will end.
For an enterprise team, the practical unit is an access relationship: one consumer, one data product or resource, an allowed purpose and a defined scope. That consumer might be an employee, a partner application or a service acting for a person. The same dataset can support different approved relationships without giving every consumer the same representation.
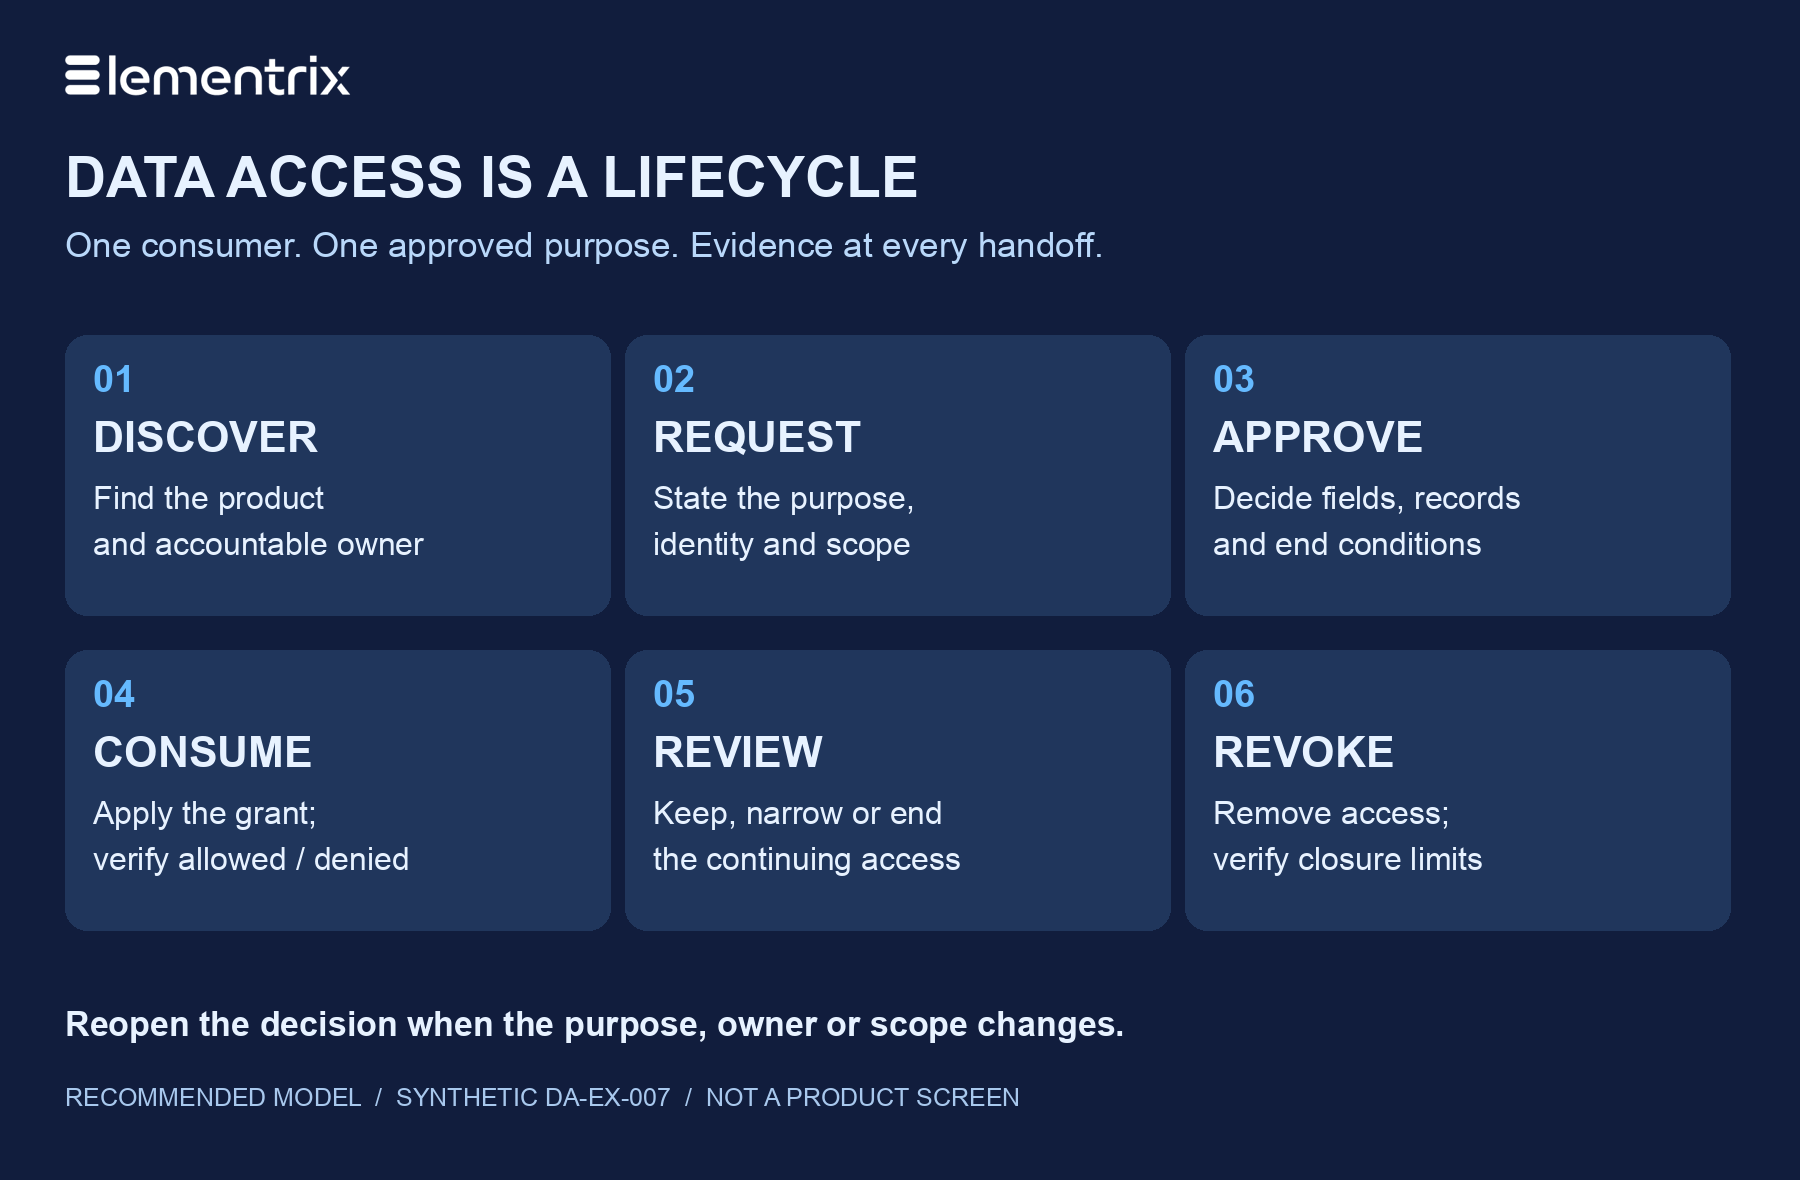
This guide uses a six-stage operating model: discover → request → approve → consume → review → revoke. It is a recommended design framework, not a claim that every organization or product implements those stages identically. The worked request, dates and fields below are synthetic examples, not customer activity or observed test results.
What data access management covers
Start by separating four responsibilities that often get mixed together. They overlap in a real architecture; drawing the boundary makes it easier to find a missing control or an unowned decision.
| Discipline | Primary question | Practical responsibility |
|---|---|---|
| Identity and access management (IAM) | Which identity is acting, and what roles or privileges belong to it? | Manage identities, credentials, authentication and entitlement lifecycle. IAM also includes access privileges; it is broader than login. |
| Data access control | May this caller perform this operation on these records and fields now? | Enforce authorization at the relevant delivery or storage boundary. |
| Data access management | How is that access requested, approved, delivered, reviewed and ended? | Connect the business decision to effective permissions and lifecycle evidence. |
| Data governance | Who owns the rules, meaning and accountability for the data? | Set ownership, classification, allowed uses and review responsibilities. |
A successful sign-in does not by itself justify a customer export. Equally, a documented approval does not prove that an API enforces the approved fields. Our data access control guide explains the enforcement layer, while data governance versus data management explains the wider operating responsibilities.
This distinction preserves the useful relationship between IAM and data controls without treating IAM as authentication alone. NIST’s IAM glossary entry includes managing roles and access privileges. Use the capabilities of your identity platform together with the data-specific decisions required by each consumer.
The six stages of a data access lifecycle
1. Discover the product and accountable owner
The consumer needs to find the data, understand its meaning and identify who can make the access decision. Discovery should expose enough metadata to judge suitability without exposing restricted records. Record the product version, owner, classification, supported interface and relevant freshness expectations. A catalog entry is a starting point, not an access grant.
If consumers cannot identify an owner or distinguish two similarly named products, the lifecycle is already blocked. Resolve that ambiguity before routing approvals. An internal data marketplace can organize discovery and access interactions, but the operating model still needs named decision makers.
2. Request a purpose and a bounded scope
Ask what task the consumer must complete, which identity will call the service, what operations it needs and which records and fields are necessary. Add an end condition or review date. “Access to customer data” is too broad to evaluate; “read account status for accounts assigned to this regional support application” gives reviewers something concrete to assess.
Distinguish a service acting independently from an application acting on behalf of a person. The appropriate user context may still constrain the latter. Use the application-level versus user-level access guide to work through that identity boundary, rather than copying a broad shared service account into a new integration.
3. Approve, narrow or reject the request
The accountable owner checks whether the purpose and requested representation are appropriate. Route security or privacy questions to the relevant reviewer when needed. Capture the decision and its rationale, including any narrower field set, record restriction, duration or operating condition. Approval should describe the scope actually allowed, not merely repeat the scope originally requested.
NIST’s least-privilege definition ties privileges to what an entity needs for its task. In an access review, that translates into a practical question: what stops working if this permission is removed? A field that is merely convenient still needs a reason to be included.
For routing, escalation and decision states in more detail, use our data access approval workflow guide. This lifecycle overview keeps those implementation details in the narrower guide.
4. Deliver and verify the approved access
Provision only the approved relationship and check it at the real consumption boundary. Verify both an allowed operation and an operation that should be denied. Compare the delivered fields and records with the decision. If a screen hides a field but the API still returns it, the data has already crossed the boundary.
Record which grant or entitlement implements the decision and which product or policy version applies. Keep unnecessary sensitive payloads out of diagnostic evidence. A useful event can identify the consumer, resource, decision and time without copying the full response. Encryption, masking, record filtering and property omission solve different problems; none replaces the need to verify authorization.
5. Review the continuing need
Review access when the consumer’s purpose, owner, role, product schema or risk changes, as well as on the planned review date. Decide explicitly whether to retain, narrow or end the relationship. Usage evidence can inform that judgment, but a frequently used permission is not automatically appropriate and an unused one is not automatically safe to leave open.
Assign the reviewer and an overdue-review response before the review starts. Microsoft’s access-review planning documentation provides a concrete example of organizing recurring or ad hoc resource reviews, choosing reviewers and applying outcomes. Treat that as a vendor-specific implementation example, not proof that the same behavior exists in another platform.
6. Revoke access and verify closure
When the approved need ends, remove the applicable grant or entitlement and verify that a new request no longer receives the restricted data. Check relevant delivery paths, including services, exports and cached representations. A workflow marked closed is not sufficient evidence that every effective permission has changed.
Document the limits of closure. Removing future access cannot recall a file already downloaded by a consumer. Credentials, sessions and cached authorization can have different lifetimes, so define and validate the expected closure behavior for the actual architecture. Record unresolved copies or retention obligations separately instead of claiming that every trace of data disappears.
Assign an owner, action and evidence at every stage
Use this table as an operating worksheet. The roles are recommended responsibilities; adapt the titles and separation of duties to your organization. The important outcome is that each decision has an accountable person and the implementation has a verifiable result.
| Stage | Responsible role | Action | Minimum useful evidence |
|---|---|---|---|
| Discover | Product owner or steward | Publish clear metadata and an approval contact. | Product identifier, owner and classification. |
| Request | Consumer owner | Describe the task, identity, scope and end condition. | Request ID, purpose, operations, records, fields and requested duration. |
| Approve | Accountable data owner; specialist reviewer when needed | Approve, narrow or reject with rationale. | Decision, approver, approved scope, conditions and review trigger. |
| Consume | Platform team and consumer implementer | Apply the grant and check allowed and denied behavior. | Grant reference, policy/product version and dated verification evidence. |
| Review | Data owner and consumer owner | Reassess the need and decide the next state. | Reviewer, evidence considered, outcome and next review or end date. |
| Revoke | Platform operator; owner confirms completion | Remove access and verify the relevant boundaries. | Closure time, effective-permission check and any residual-copy limitation. |
For example, HR managers may have an approved payroll purpose while a general manager needs a narrower workforce view. A support application may need an account status without a tax identifier. These are design examples: role names alone do not establish permission. The purpose, record population and allowed representation must still be specified.
Worked example: a regional support access request
Synthetic request DA-EX-007: a regional support application needs to route active accounts to its service queue. Its owner requests read access to an account-status product for a 30-day evaluation. This is a proposed review exercise; the dates and outcomes below do not report a live implementation or customer result.
| Stage | Decision or action in this example | What the team should check |
|---|---|---|
| Discover | Choose Account Status v1 and identify the named product owner. | Does the product describe status meaning, refresh time and the approval contact? |
| Request | Read account_id, account_status, service_region and last_updated_at for the assigned region. | Is the application identity specific, and is a 30-day evaluation justified? |
| Approve | Owner approves the regional record boundary and four fields; excludes contact email, billing address and tax ID. | Is the approved scope recorded separately from the original request? |
| Consume | Platform team applies the approved representation; consumer validates the routing task. | An allowed regional record should return only approved fields; an out-of-region request should not disclose the record. |
| Review | Owner reviews the evaluation before the end date and decides whether it still has a purpose. | Is extension an explicit new decision rather than a silent continuation? |
| Revoke | If the evaluation ends, remove the relationship and test a new request. | Does the actual delivery boundary deny access, and are any previously exported copies recorded? |
The four fields are chosen for this fictional task, not as a universal account schema. If a consumer later needs to contact a customer, reopen the purpose and representation decision. Do not quietly add contact details to the routing response. Our API data minimization worksheet expands this same kind of field-selection exercise with before-and-after JSON and acceptance checks.
Keep the request, decision, implementation and closure references connected. That connection lets a reviewer trace why access exists and whether the configured permission still matches the approved business need. It also makes the handoff between the owner, platform operator and consumer easier to inspect.
Measure completion and control quality together
A short approval time is useful only if the resulting access is appropriate. Start with a few measures whose timestamps and denominators your team can actually observe. The definitions below are suggestions, not benchmark claims or Elementrix performance results.
| Measure | Suggested definition | Interpretation limit |
|---|---|---|
| Request-to-usable-access time | Time from a complete request to verified usable access; show median and a tail percentile. | Separate time waiting for missing information from review and provisioning time. |
| Owner coverage | In-scope products with a named active approval owner divided by all in-scope products. | An owner name alone does not prove an effective review. |
| Overdue access reviews | Open reviews past their agreed due date divided by reviews due in the period. | Record the policy response; a low count should not hide unstarted reviews. |
| Scope verification coverage | New or changed grants with recorded allowed/denied checks divided by grants requiring those checks. | Coverage is evidence of a check, not proof that every possible path was tested. |
| Closure verification time | Time from the end-access decision to verified denial at the defined boundaries. | State exclusions, such as already downloaded files and independently retained copies. |
Use a consistent reporting window and report missing evidence as missing. If the team cannot connect grants to owners or review dates, first establish that inventory. Avoid inventing a baseline, savings estimate or compliance percentage from the presence of a workflow.
Connect the lifecycle to the wider data operating model
The existing guide’s core advice remains useful: classify sensitive data, apply least privilege, make policy decisions consistent and monitor access. RBAC can group permissions around responsibilities; ABAC can use relevant attributes to refine a decision. The design still needs trustworthy identity and attribute sources, clear enforcement boundaries and a review process when those inputs change.
A governed data product can make the approved representation and its meaning easier to manage, but packaging alone does not prove authorization, quality or freshness. Read what a data product contains and the broader data governance guide when those foundations need attention. Keep specialist implementation decisions in the linked workflow, identity and field-selection guides.
Start with one product and one consumer. Walk through the six stages with the accountable owner and platform team, identify where the decision or evidence is missing, and agree who will close that gap. This is more actionable than buying a category label without establishing how an approved relationship will work.
Request an Elementrix demo and bring one data product and one consumer use case. Use the lifecycle worksheet to discuss discovery, approval, delivered scope, review and closure, and confirm which steps the current implementation supports and which remain part of your operating process.